Open, InspectableSecure Silicon
PRESENTING
HoloDi S1 SoC
HoloDi is a secure System-on-Chip (SoC) built on open-source RISC-V architecture with secure element class features
Based on baochip-1x
PACKAGE LID
BOND WIRE LAYER
SILICON DIE
SUBSTRATE
CONTACT PADS
Exploded view of the HoloDi S1 package. From the top: package lid, bond wire layer, silicon die, substrate, contact pads.
WHAT WE DO
HoloDi is a secure System-on-Chip (SoC) built on open-source RISC-V architecture with secure element class features*
The HoloDi S1 SoC functions as a transparent and sovereign security processor, engineered for independent verification across the entire stack. By enforcing critical safety protocols directly in silicon, HoloDi provides a verifiable safeguard for essential infrastructure. We focus on customized firmware and attestation for your secure hardware approach.
*based onbaochip-1x
HARDWARE
A chip that can be independently inspected, verified, and manufactured sovereignly.
Auditable all the way down to the physical silicon: the chip design is open, the firmware is reproducible, and the final fabricated die can be optically inspected.
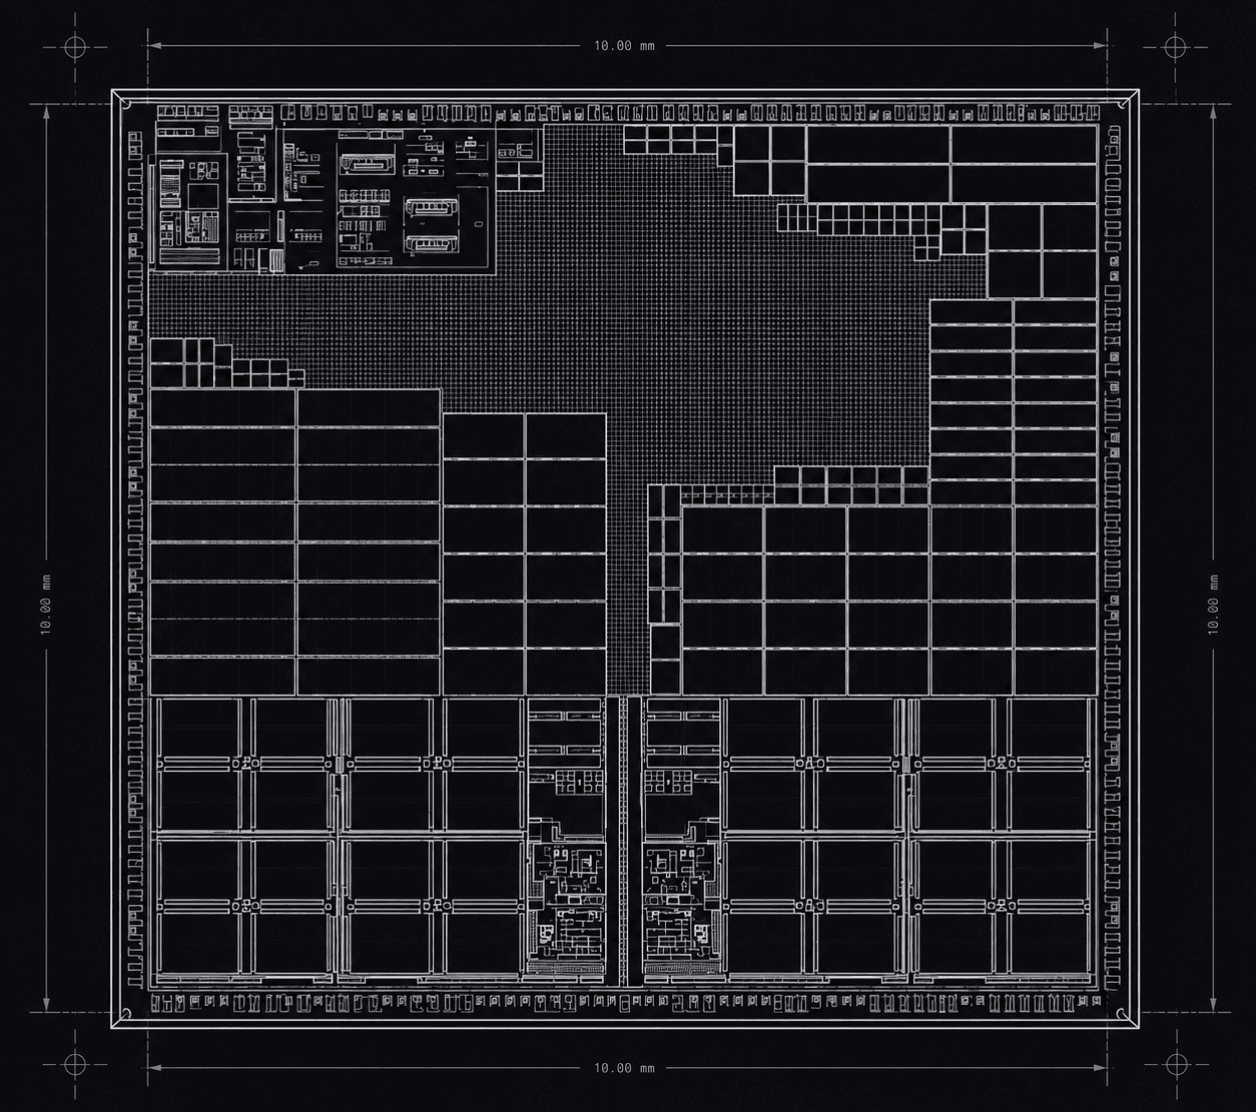
- RRAM
- 4 MiB, Non-volatile on-die
- SRAM
- 2 MiB + 256 KiB I/O with ECC
- CPU CORE COMPLEX
- RISC-V RV32-IMAC@350 MHz Full MMU with paged virtual memory & Zkn Crypto ext
- ALWAYS ON
- RTC; power reset; WDT
- BIO
- I/O coprocessor 4 × PicoRV @ 700 MHz
- ANALOG/MS
- PLL; USB HS; ADC; reg
- CRYPTO
- AES, RSA/ECC, SHA-2/3
- LOW LEAKAGE
- 22 nm TSMC Ultra Low Leakage
- KEYS + TRNG
- Key store, entropy & one-time counters
FIRMWARE: ENFORCED BY HARDWARE
Security Peripherals as building blocks for securing systems.
Auditable all the way down to the physical silicon: the chip design is open, the firmware is reproducible, and the final fabricated die can be optically inspected.
- Signed & Measured Boot
- Only Authenticated firmware & code runs
- Remote Attestation
- Remotely proves what’s exactly running
- On-die Key Store + Hardware TRNG
- Random Keys generated & Kept on-chip
- Trusted Time + Monotonic counters
- Anti-rollback & Freshness
- Cryptography: AES. RSA/ECC, SHA-2/3
- Encrypt, sign and verify at the hardware level
- Quantum Secure: ML-KEM, ML-DSA
- Post-quantum Ready
- Glitch/fault sensors, ECC memory
- Active Tamper Mesh + Sensors for defence
- Key Zeroize on Tamper
- Instant Key Zeroize on capture attacks
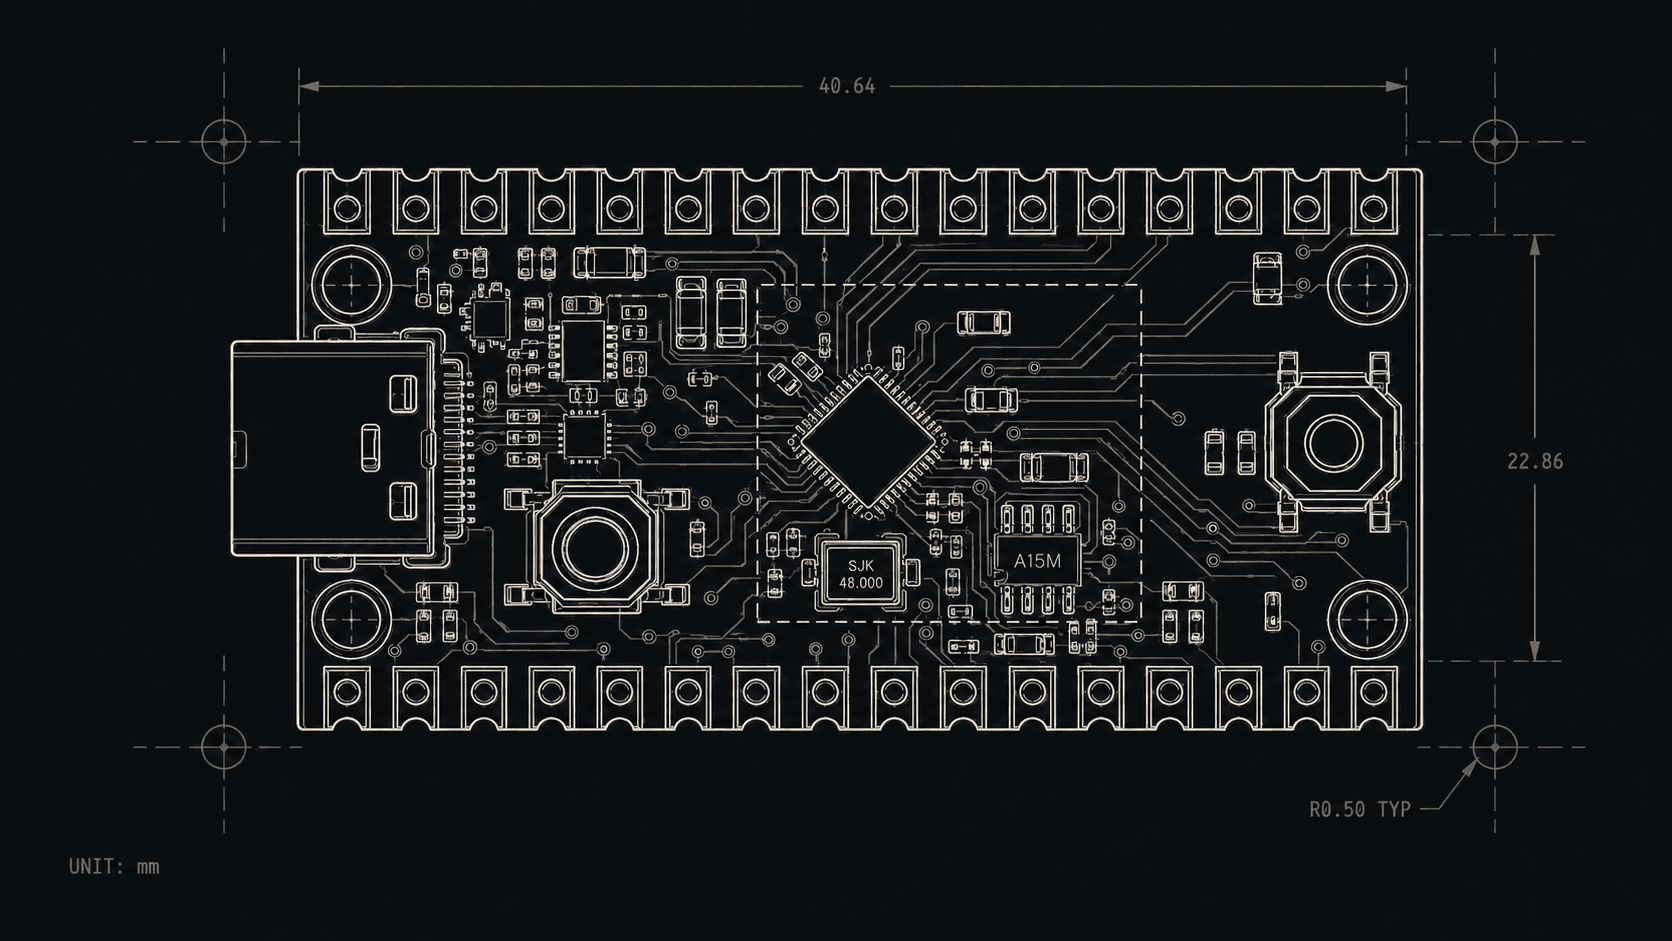
An isolated hardware anchor
root of trust
FIRMWARE: ENFORCED BY HARDWARE
Use cases & Application
Auditable all the way down to the physical silicon: the chip design is open, the firmware is reproducible, and the final fabricated die can be optically inspected.
Autonomous Defence Systems
A platform the enemy can't take over. Commands signed in hardware, firmware attested before flight, keys that vanish on capture.